Compliance
SOC 2, ISO 27001 & PCI DSS – without the overwhelm
We help 20–100 person companies understand what's required, close the security gaps, write the policies and get ready for a successful audit or assessment.
Get Compliance Help →See the path to compliance
Sound familiar?
Suddenly, compliance is your problem
A prospect sends a security questionnaire
And the deal depends on your answers.
Your cyber insurer asks for documentation
Policies, controls and proof that they work.
A contract requires SOC 2, ISO 27001 or PCI DSS
With a deadline attached.
Now your team is expected to produce policies, risk assessments, technical controls and evidence that may not exist yet. We make it manageable.
How it works
A practical path to compliance
Discover
We identify your requirements, systems, data, vendors and business processes.
Assess
We compare your environment against the standard and document the gaps.
Remediate
We implement the policies, procedures and technical safeguards to close them.
Prepare
We organize evidence, test controls and get your team ready for the assessment.
Maintain
We keep your program current after the audit, report or certification.
How Tech Plus helps
From first questionnaire to clean audit
Scoping & readiness assessment
We identify what's in scope – standards, contracts, systems, data and locations – and measure your current program against it. You get a practical roadmap showing:
- What's already in place
- What's missing
- Which risks to address first
- Who owns each requirement
- What documentation is needed
- Which technical changes are required
- What evidence to collect
- How to prepare for the audit
Security policies & documentation
Compliance takes more than security software – you also have to define how information is protected and show you follow it. We tailor documentation to how your company actually works: a usable program, not generic templates sitting unread in a folder.
Technical remediation
Once the gaps are clear, our engineers implement the controls your standard calls for.
Evidence collection & audit prep
Having controls is only half the job – you have to prove they're working. We organize the records, screenshots, reports, logs, training records and approvals auditors ask for, and work directly with your auditor, CPA firm, QSA or certification body to answer technical questions and address findings.
Ongoing compliance management
Compliance isn't a one-time project. Accounts change, employees leave, vendors are added and new vulnerabilities appear – we keep your program current.
Cyber insurance
Could you answer these today?
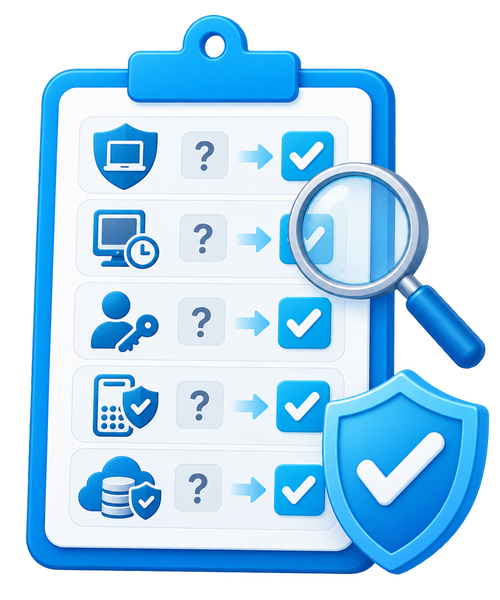
Questions straight from a typical cyber insurance questionnaire:
- 1Do you use EDR or MDR tools on all workstations and servers?
- 2What percentage of your systems run legacy or end-of-life operating systems?
- 3Do standard users have local administrator rights on their machines?
- 4Is MFA required for all remote access (VPN, RDP, dial-in)?
- 5Are your backups stored in an air-gapped, offline or immutable repository?
Not sure? We'll handle it.
Insurance forms are often cryptic and confusing – and many ask whether you have written policies in place. We have ready-made templates for most of them and tailor them to your company.
Let's talk
Get audit-ready with confidence
Whether it's a questionnaire due Friday or a SOC 2 audit next year, we'll give you a clear plan to get there.
Get compliance help
Tell us which standard you're facing and we'll map out what it takes.